Informal documentation of prompts and setups that have been successful in finding malicious infrastructure. The majority of the prompts are going through a modified opencode, GLM5.3 and MCP's built on the API's of Validin/URLScan.
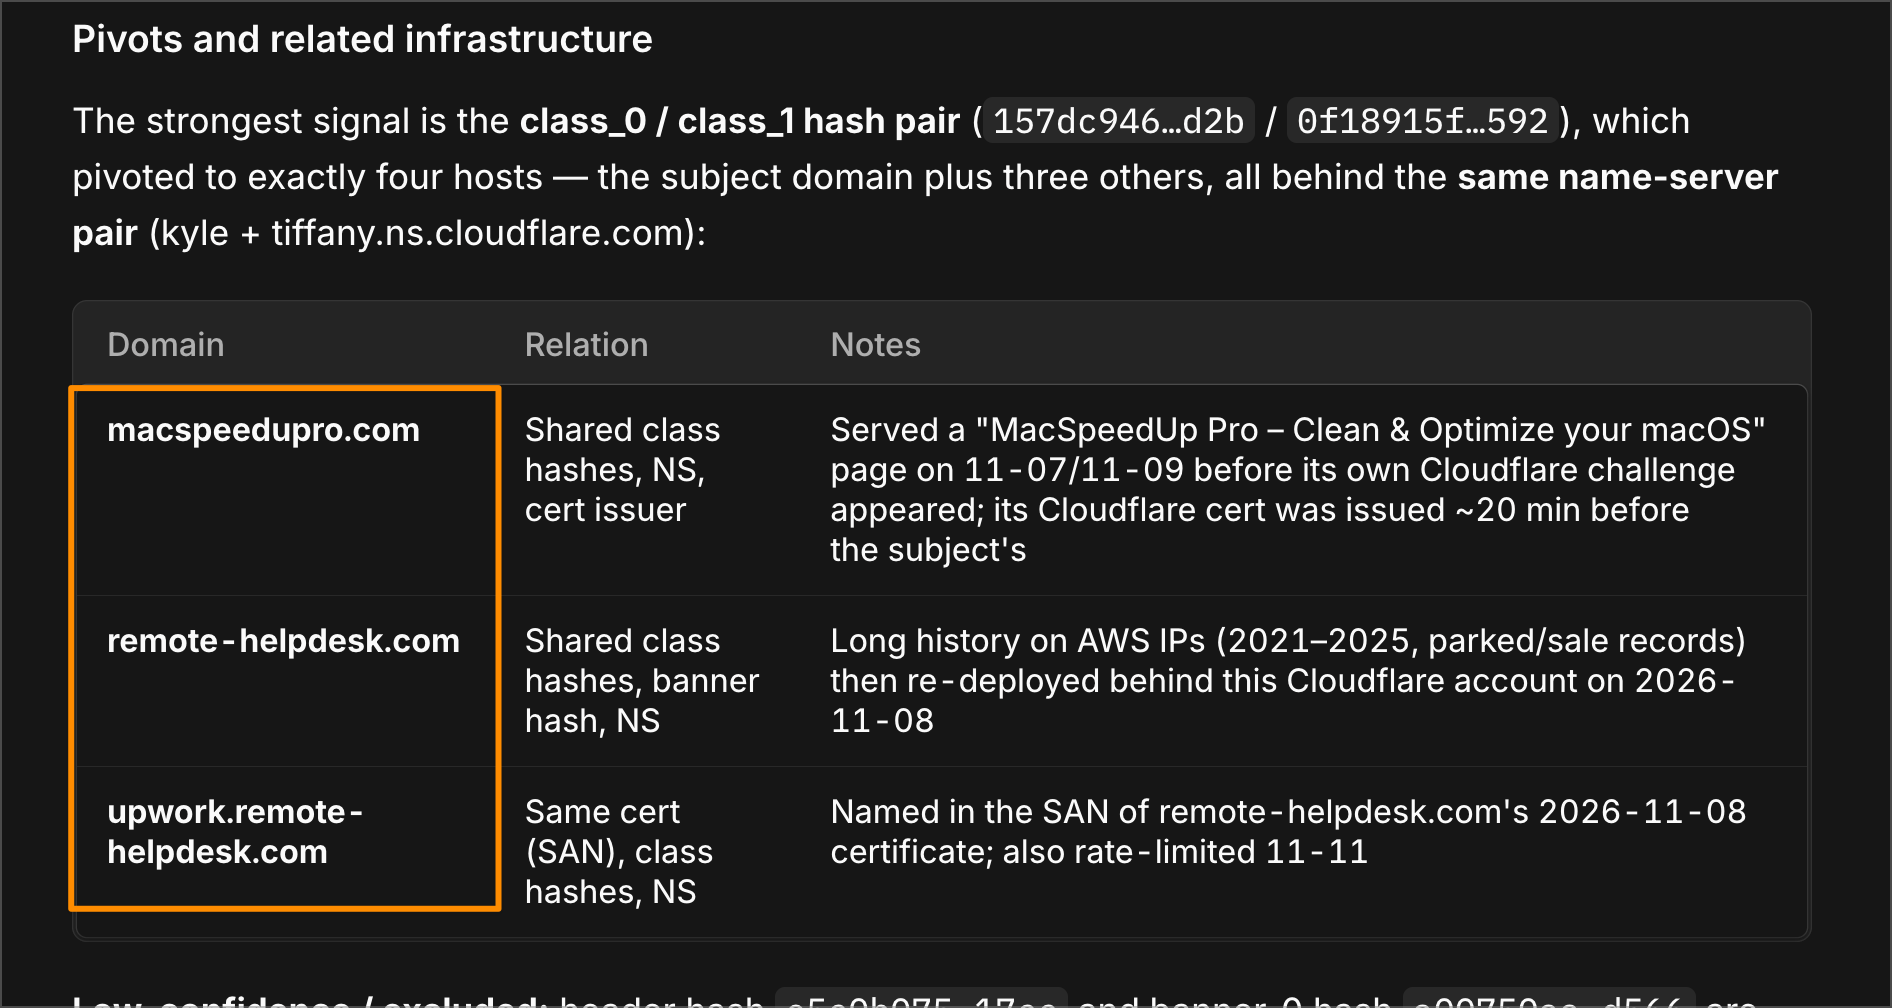
LLM was able to use similarities in the class hash to identify similar infrastructure.
Take a look at browser-architecture-sync[.]com, attempt a pivot(s) and list out related infrastructure that you find. Group into categories of high/medium/low confidence.
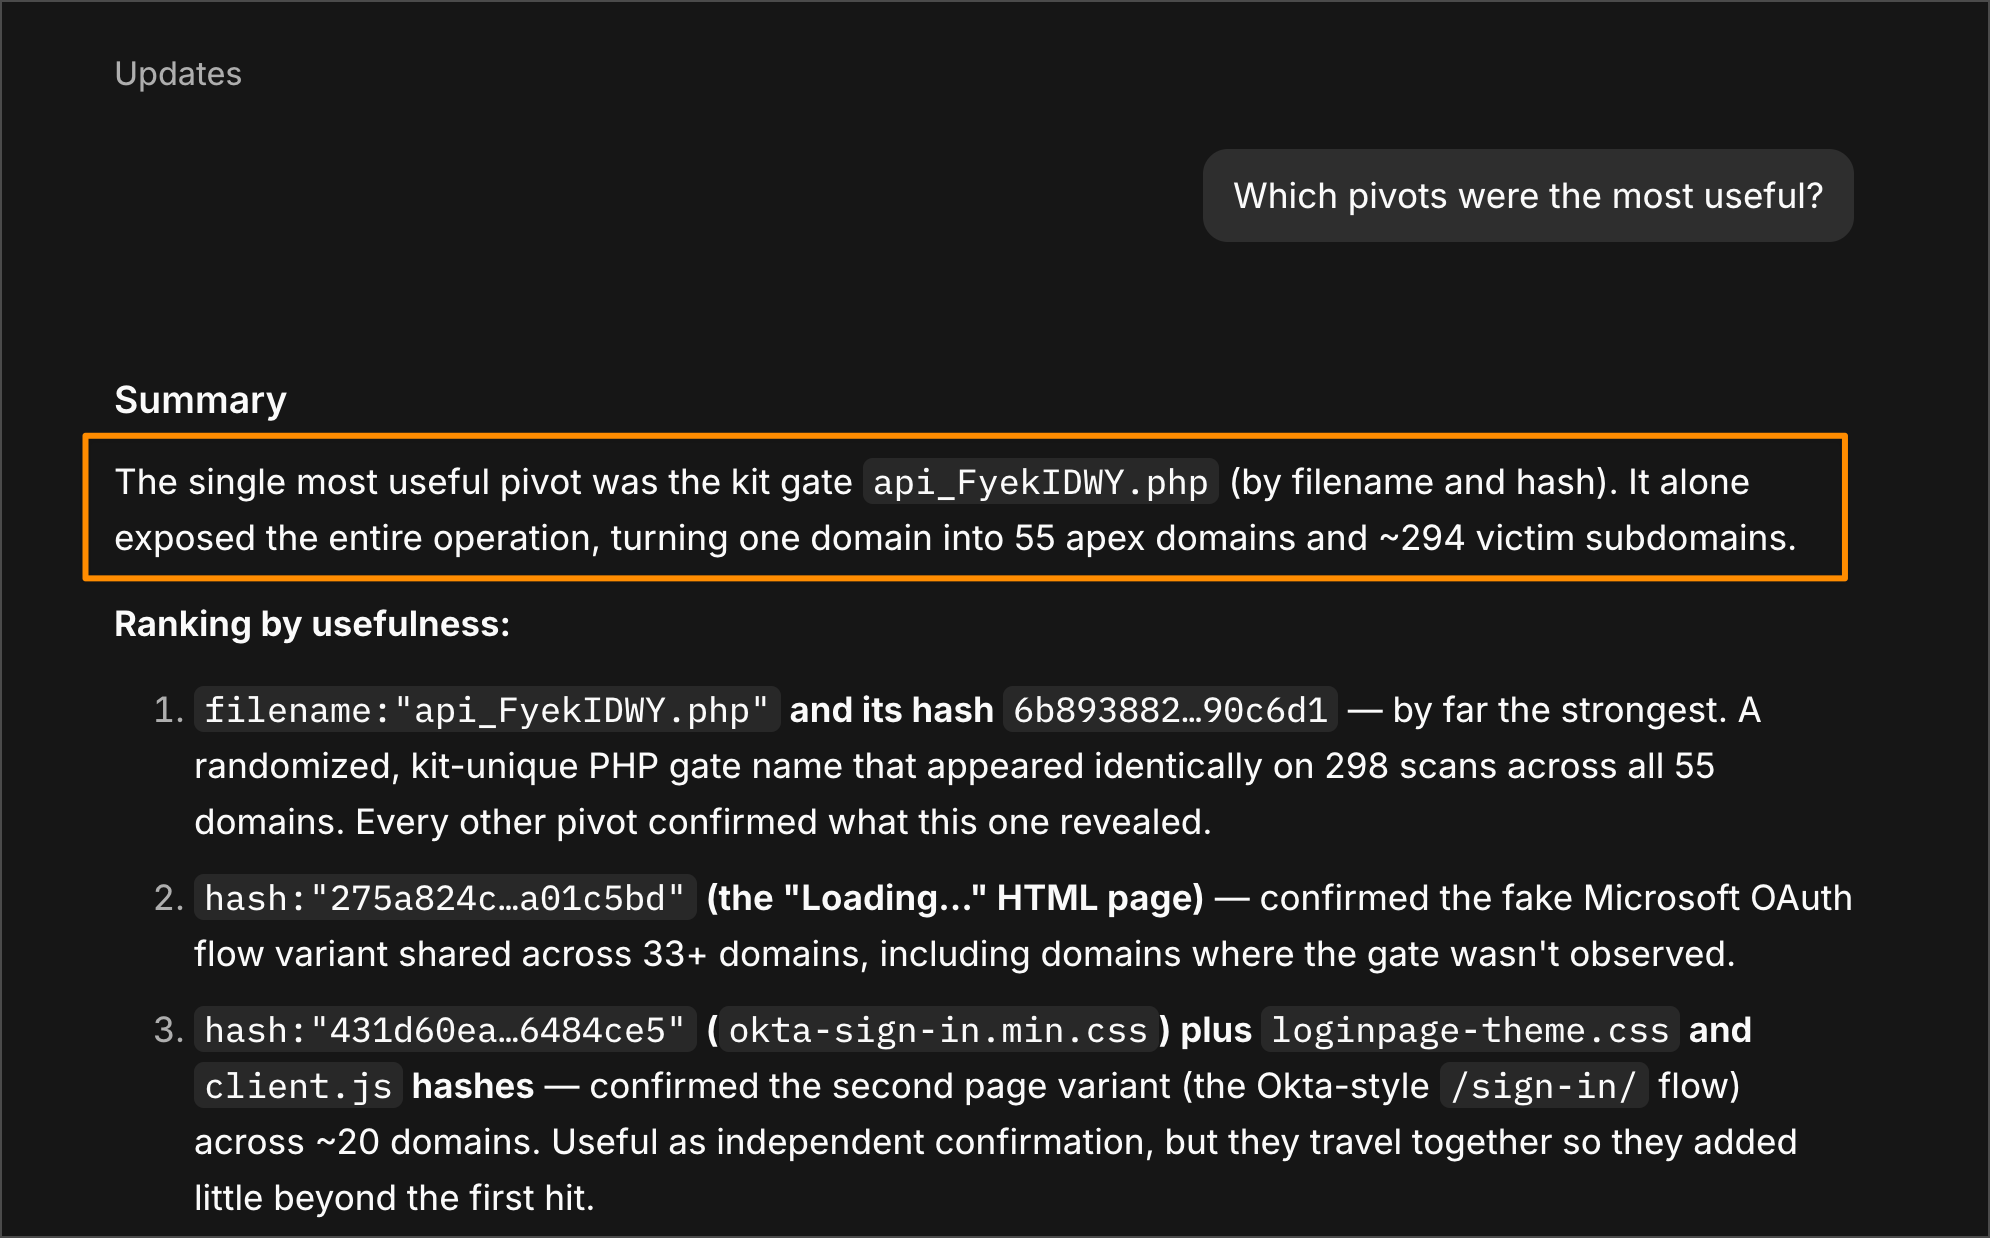
LLM was able to find related infrastructure through similarities in one of the files loaded by the majority of the campaigns pages. Both the filename and hash were found to be useful pivots.
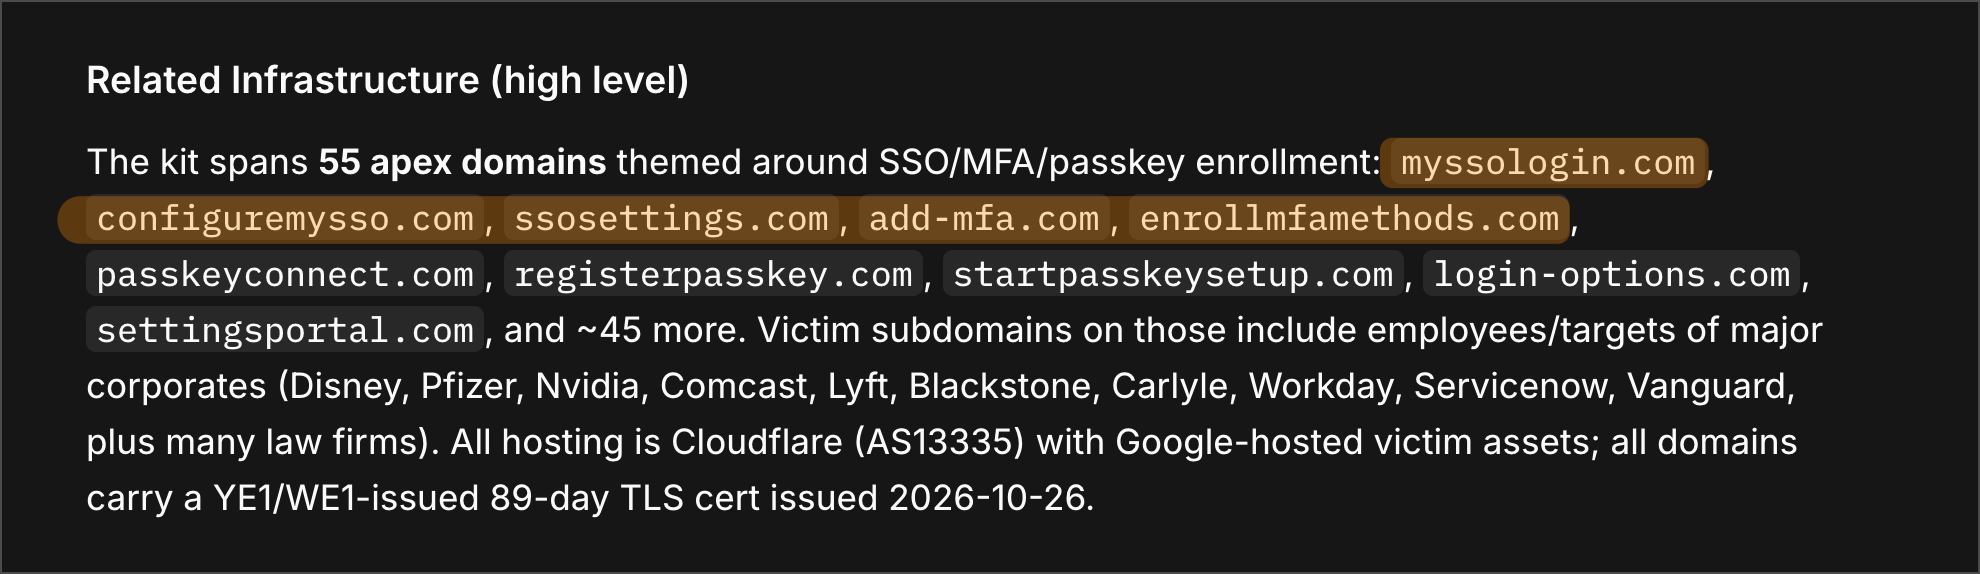
Take a look at myssosetup[.]com. List out all loaded files, subdomains and url paths. Construct pivots and identify related infrastructure. List out all pivots used, and output results in groups of high/medium/low confidence.
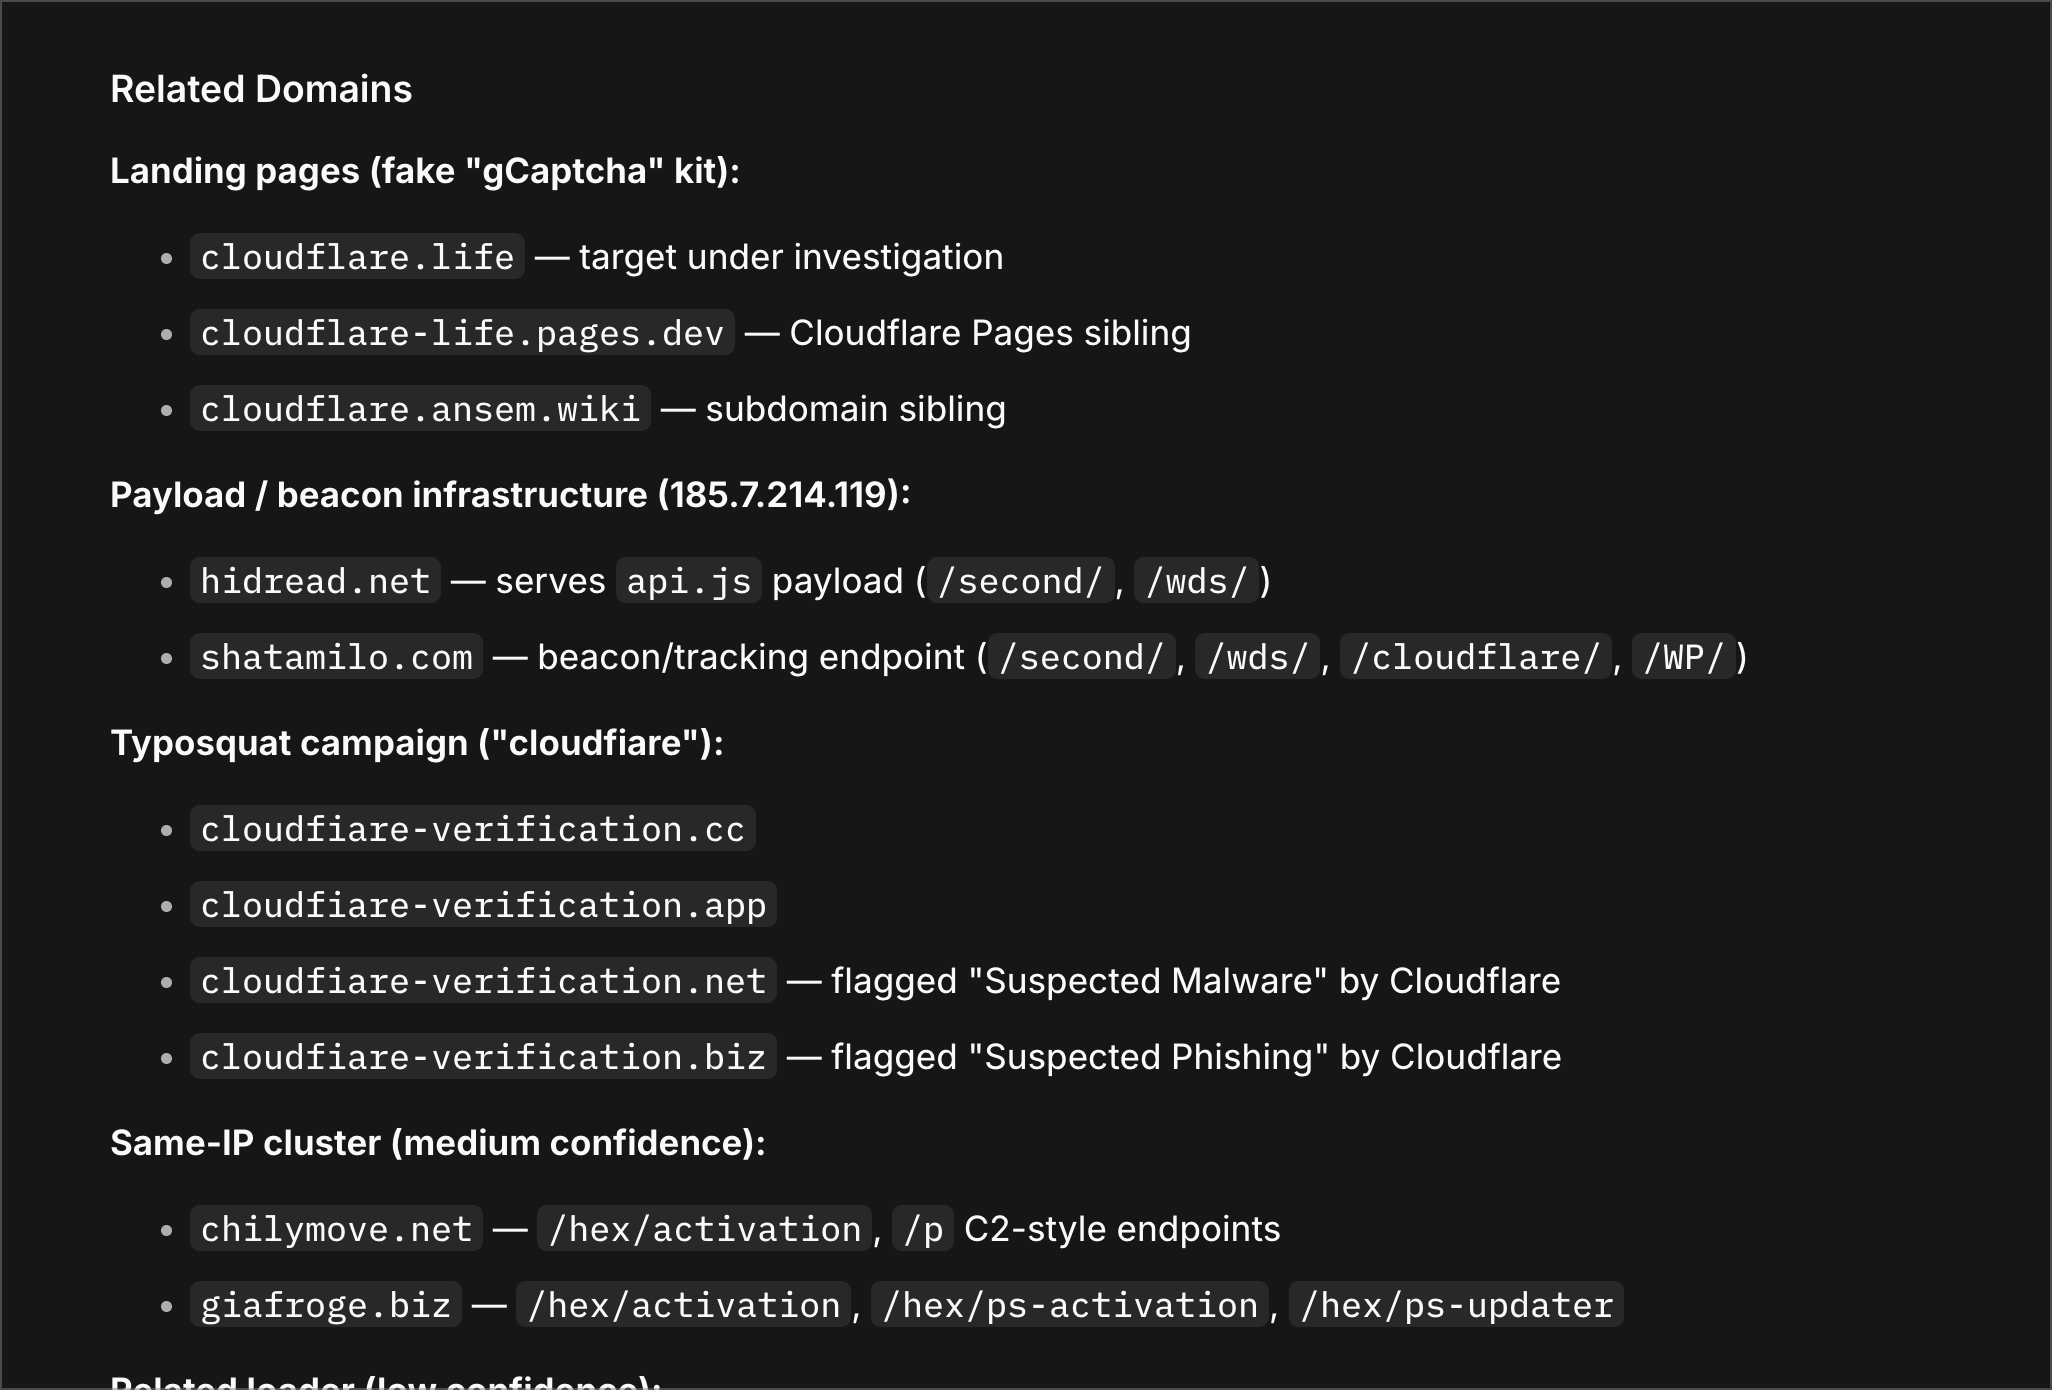
Test 3 - Validin Fake Cloudflare Infra.
Initial indicator shared by Anurag/@malwarehunterr. (Link)
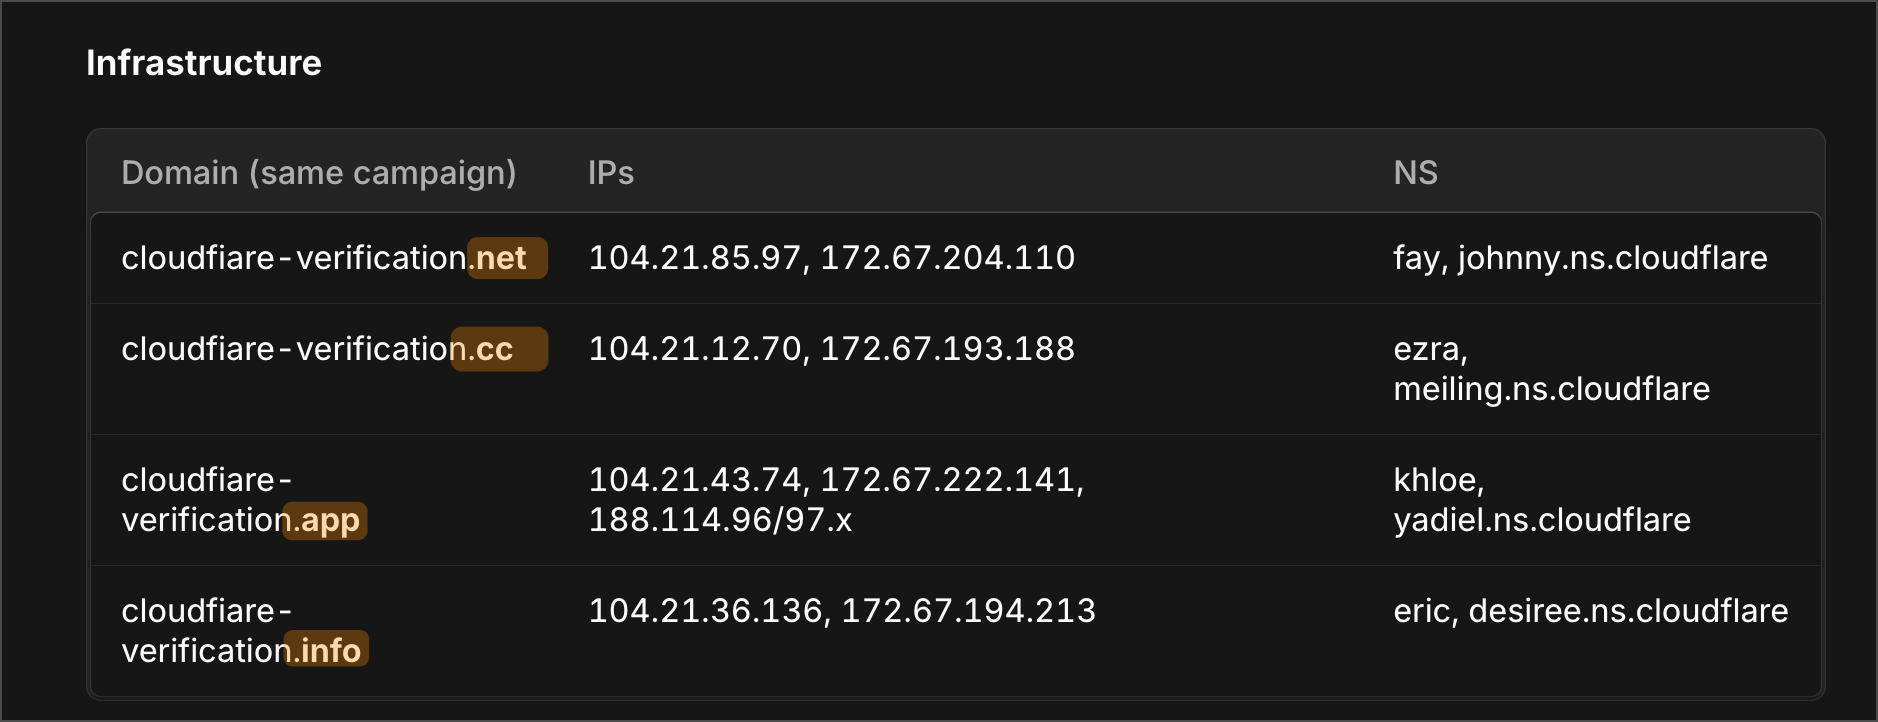
Tell me about cloudfiare-verification[.]net, find related infrastructure. Pivot on all available values.
Test 4 - URLScan fake Cloudflare Infra.
Take a look at cloudflare.life. Find any related infrastructure. Focus on external files, domains and hashes related to content being loaded by the page. Document findings. Group results into high/med/low confidence.