Content Paint

Recent Posts

Cobalt Strike Malware Analysis With CyberChef and Emulation - .HTA Loader Example

Decoding a .hta script with CyberChef and analysing Shellcode with the SpeakEasy Emulator.
Ghidra Tutorial - Using Entropy To Locate Cobalt Strike Decryption Functions

Using Ghidra Entropy Analysis to Identify a decryption function.
How To Decode Visual Basic (.vbs) Malware - DarkGate Loader

Demonstrating basic techniques for decoding a darkgate .vbs loader.
How to Write Yara Rules For DotNet Malware

How to develop Yara rules for .NET Malware. Utilising IL instructions and associated bytecodes.
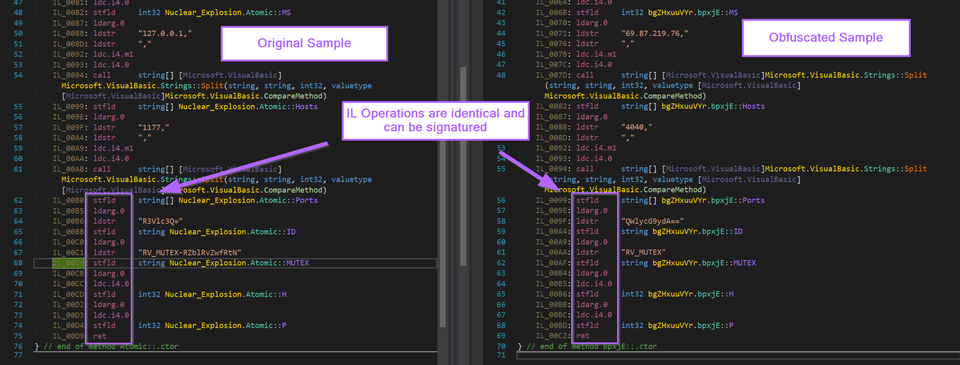
How To Write a Simple Configuration Extractor For .NET Malware - RevengeRAT

Introduction to dotnet configuration extraction. Leveraging RevengeRat and Python.
How To Write Yara Rules For Malware - Practical Examples

Practical examples and breakdowns of indicators that can be used to produce effective yara rules.

Your link has expired. Please request a new one.
Great! You've successfully signed up.
Welcome back! You've successfully signed in.
Success! You now have access to additional content.