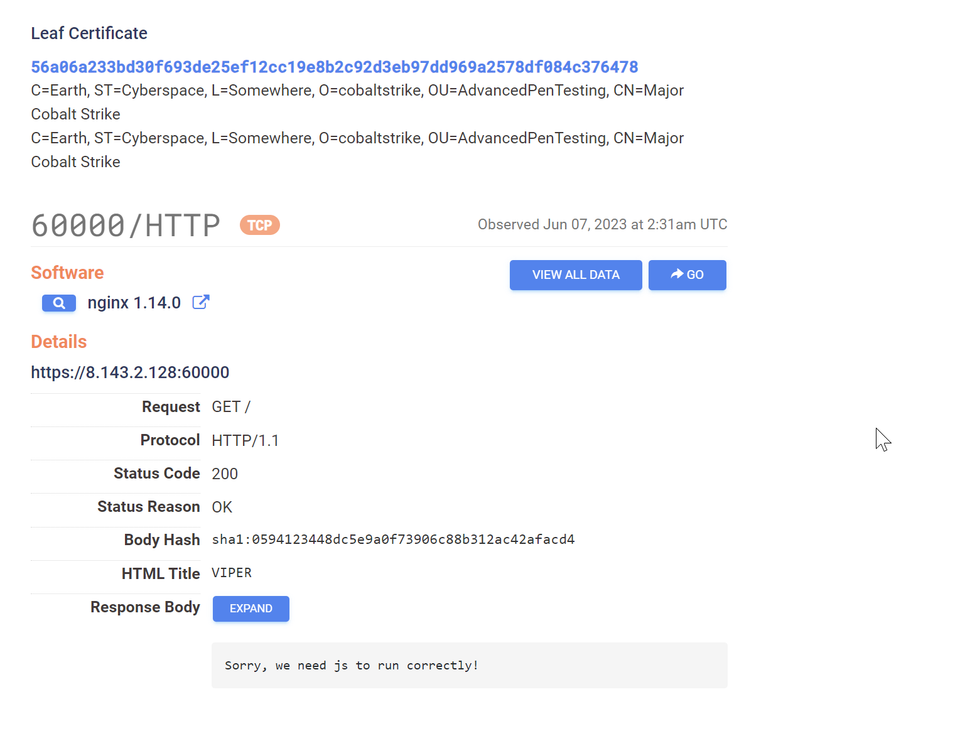
Threat Intelligence Queries with Censys.
Useful code snippets for developing dotnet configuration extractors.
Decoding malware loaders using Procmon and Cyberchef. Utilising Powershell to retrieve additional payloads and free online tooling to identify the malware family.
An informal page for storing Censys/Shodan queries
Identifying Amadey Bot Servers Using Shodan.
Identification of Laplas infrastructure with Shodan and Censys.