Content Paint

Recent Posts

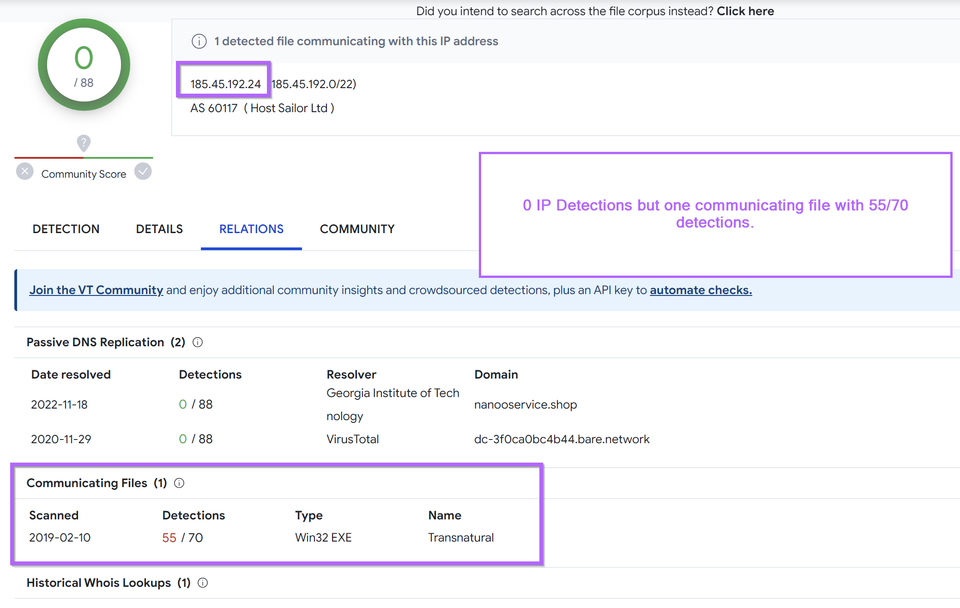
Identifying PrivateLoader Servers with Infrastructure Queries

Refining Queries and Identifying Suspicious servers using Censys.
Ghidra For Malware Analysis - Pivoting from String Cross References

Leveraging Ghidra to establish context and intent behind suspicious strings.
Beginner Ghidra Guide - Manual Shellcode Decryption

Manually Reversing a decryption function using Ghidra, ChatGPT and CyberChef.
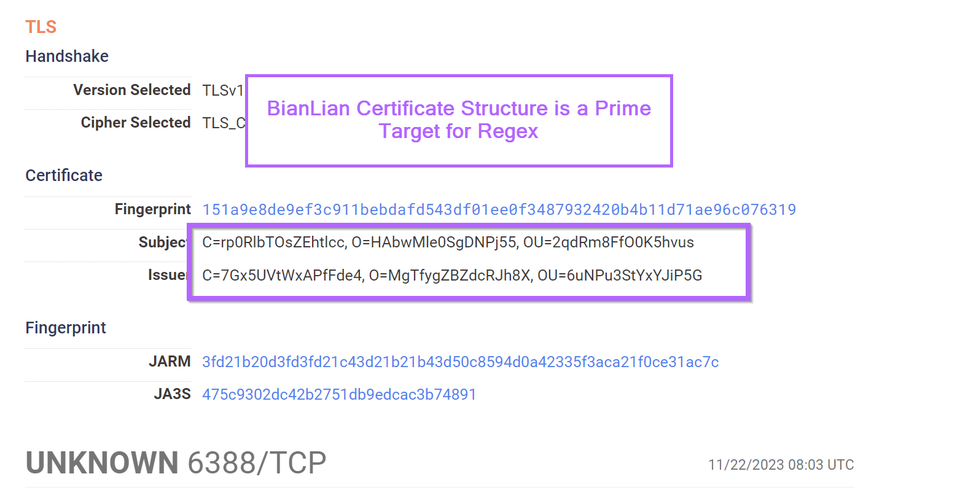
Practical Queries for Malware Infrastructure - Part 3 (Advanced Examples)

More interesting and practical queries for identifying malware infrastructure.
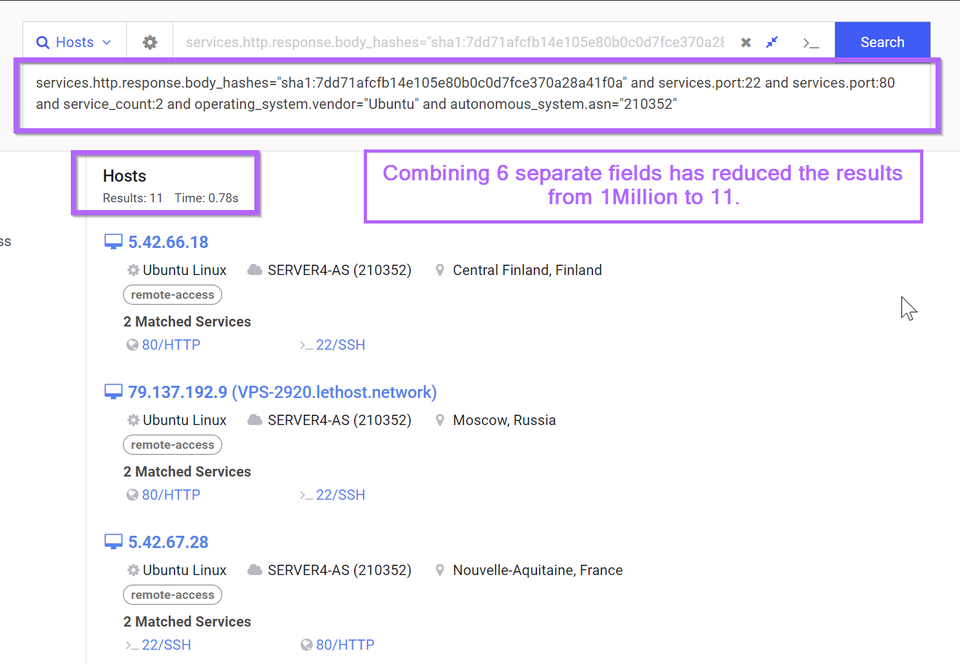
Combining Pivot Points to Identify Malware Infrastructure - Redline, Smokeloader and Cobalt Strike

Identifying Malware infrastructure by combining weak pivot points.
How To Use Garbageman To Extract C2's From Dotnet Malware

Extracting C2 configuration using the Garbageman .NET analysis tool

Your link has expired. Please request a new one.
Great! You've successfully signed up.
Welcome back! You've successfully signed in.
Success! You now have access to additional content.