Dnspy
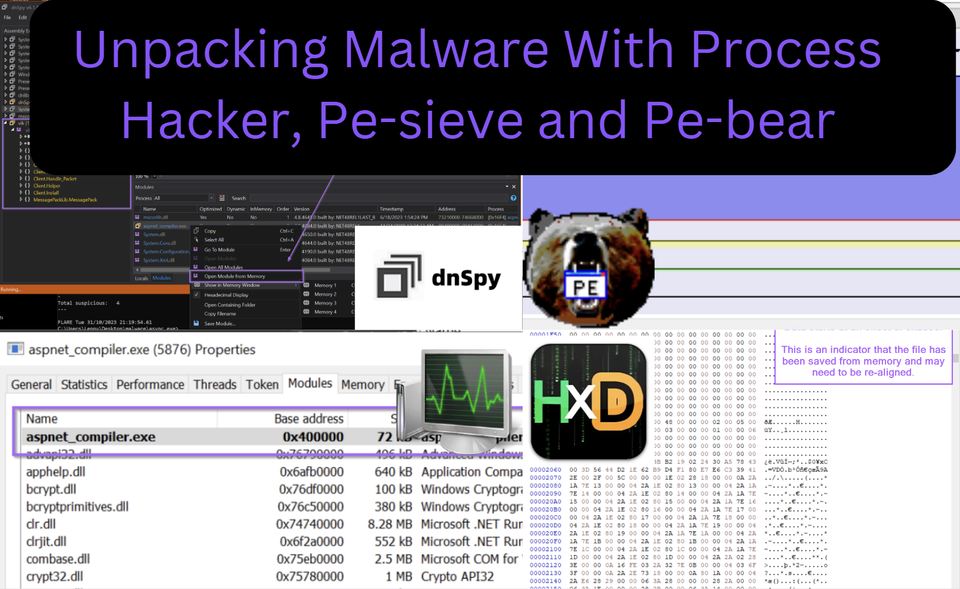
Demonstrating three additional methods for obtaining unpacked malware samples. Using Process Hacker, Pe-sieve, Hxd and Pe-bear.
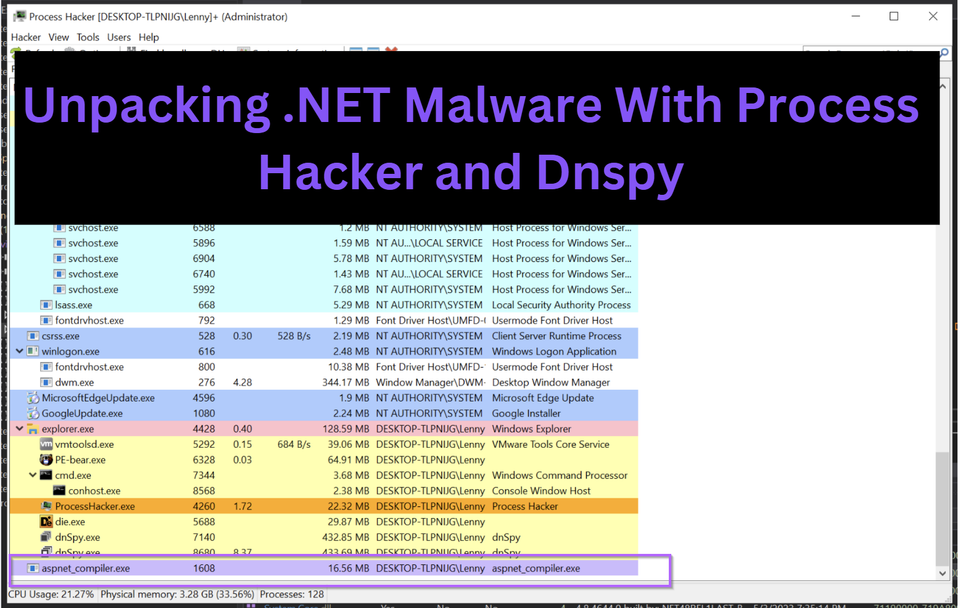
Unpacking an Asyncrat loader using Process Hacker and Dnspy
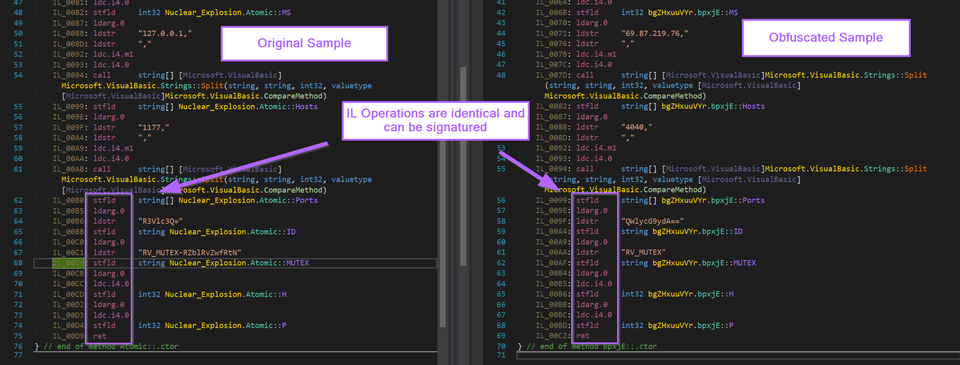
How to develop Yara rules for .NET Malware. Utilising IL instructions and associated bytecodes.
Introduction to dotnet configuration extraction. Leveraging RevengeRat and Python.
Extraction of Quasar C2 configuration via Dnspy, and using this information to pivot to additional servers utilising Shodan and Censys.