Content Paint

Threat Intelligence

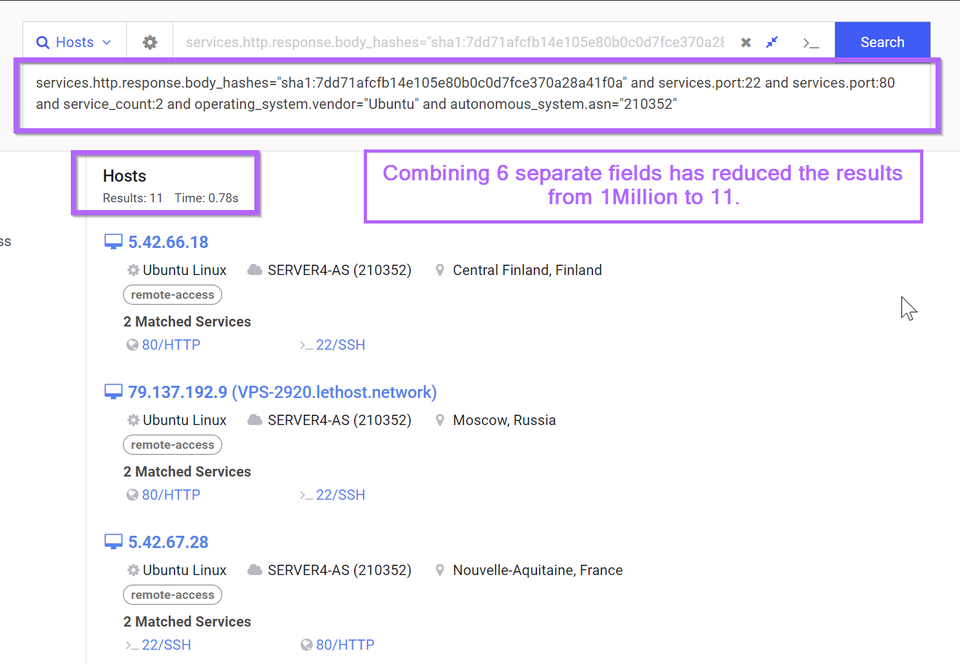
Combining Pivot Points to Identify Malware Infrastructure - Redline, Smokeloader and Cobalt Strike

Identifying Malware infrastructure by combining weak pivot points.
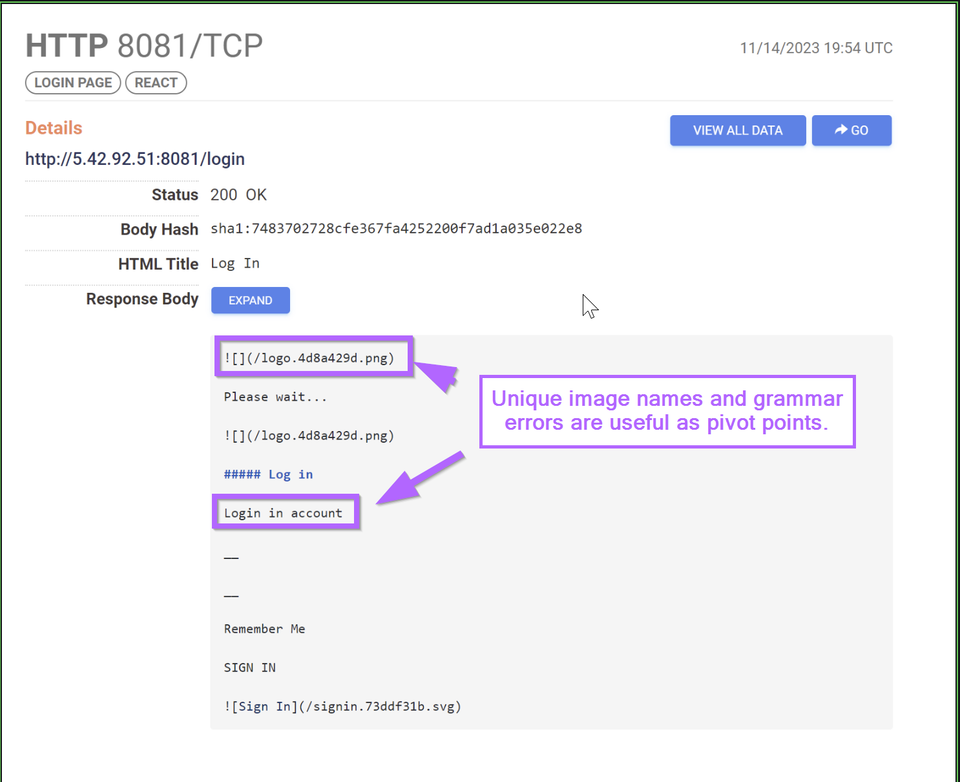
Identifying Simple Pivot Points in Malware Infrastructure - RisePro Stealer

Identifying Simple pivot points in RisePro Stealer Infrastructure using Censys.
Practical Queries for Identifying Malware Infrastructure - Part 2

Threat Intelligence Queries with Censys.
How To Track Malware Infrastructure - Identifying Laplas Infrastructure Using Hardcoded TLS Certificates

Identification of Laplas infrastructure with Shodan and Censys.

Your link has expired. Please request a new one.
Great! You've successfully signed up.
Welcome back! You've successfully signed in.
Success! You now have access to additional content.