Content Paint

Threat Intelligence

Introduction To Malware Infrastructure Analysis With Passive DNS

Malware Infrastructure Tracking Using Passive DNS Intelligence.
Practical Queries for Identifying Malware Infrastructure With FOFA

Identifying malware infrastructure with the FOFA scanner.
Identifying Qakbot Servers with Regex and TLS Certificates

Catching 83 Qakbot Servers using Regular Expressions.
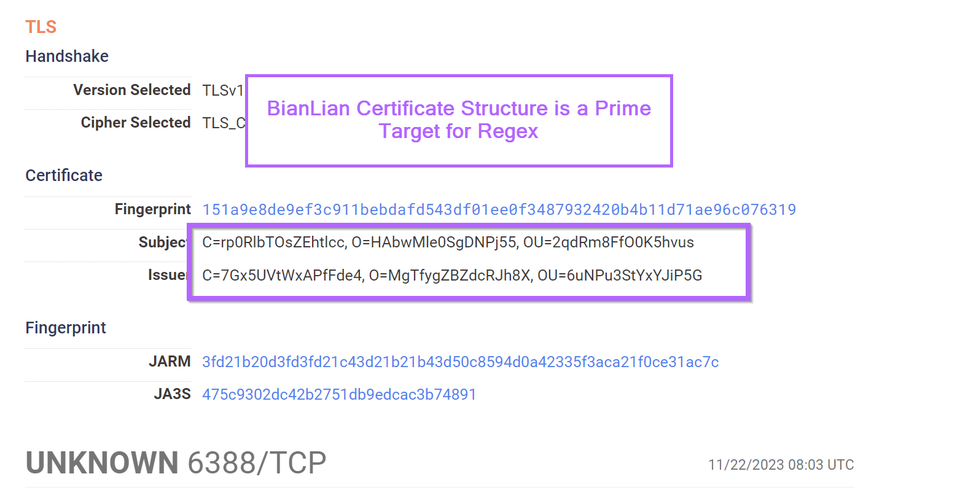
How To Build Advanced Threat Intelligence Queries Utilising Regex and TLS Certificates - (BianLian)

Creating Regex Signatures on TLS Certificates with Censys.
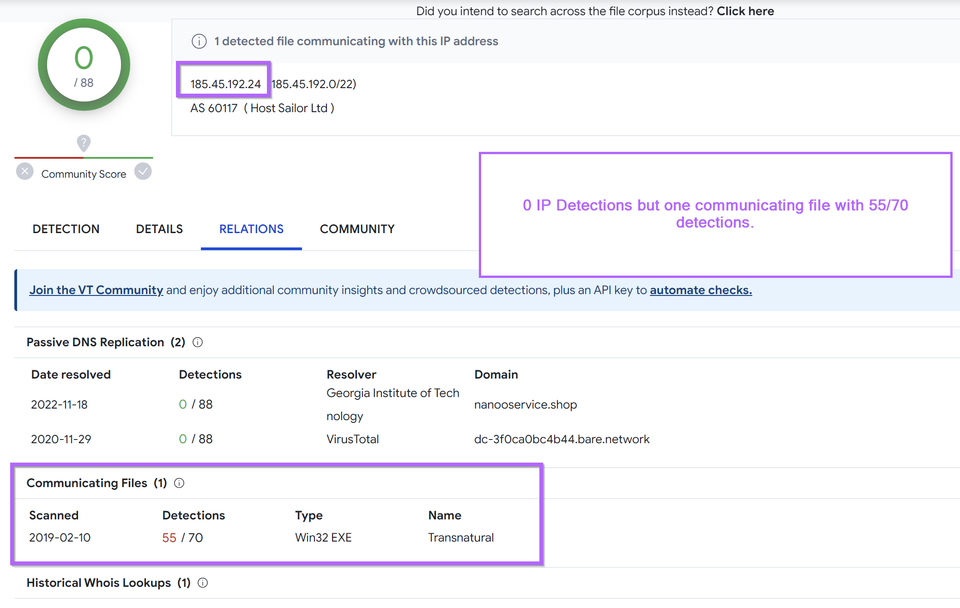
Identifying PrivateLoader Servers with Infrastructure Queries

Refining Queries and Identifying Suspicious servers using Censys.
Practical Queries for Malware Infrastructure - Part 3 (Advanced Examples)

More interesting and practical queries for identifying malware infrastructure.

Your link has expired. Please request a new one.
Great! You've successfully signed up.
Welcome back! You've successfully signed in.
Success! You now have access to additional content.